Your PKI,
one install away.
The self-hosted certificate authority with a modern web UI. Create, manage, discover and automate your certificates. No YAML, no CLI expertise needed.
docker run -d -p 8443:8443 neyslim/ultimate-ca-manager Latest release v2.243 , 21 October 2026
Up and running in 60 seconds
Choose your platform. One command, full PKI.
docker run -d --restart=unless-stopped \
  --name ucm \
  -p 8443:8443 \
  -p 8080:8080 \
  -v ucm-data:/opt/ucm/data \
  -v ucm-config:/etc/ucm \
  neyslim/ultimate-ca-manager:latest
Then open
https://localhost:8443
and log in with
admin /
changeme123
Need FIPS? Use the
-fips
image with
UCM_FIPS=1,
or the packages on RHEL 9 and Ubuntu 24.04 Pro:
FIPS mode guide.
A complete PKI platform,
not just a CLI tool.
Everything from your root CA down to network discovery, in one self-hosted app.
CA Hierarchy
Build complete trust chains from the web UI, without openssl gymnastics.
- Root & intermediate CAs
- Offline, HSM-backed or externally signed
- RFC 5280 name constraints
- Revoke an intermediate from its parent
Certificate Lifecycle
Issue, sign, renew, revoke and export, in bulk when you need it.
- In-place renewal keeps the same ID
- PKCS#12, PEM, DER and JKS export
- Approval workflows on every path
- RFC 5280 / CA-B Forum linting
ACME Server
RFC 8555 with ARI, EAB and named profiles. certbot, acme.sh, Caddy, cert-manager.
Windows Enrollment
Autoenrollment over XCEP/WSTEP, or sign through an existing AD CS.
SCEP & EST
RFC 8894 and RFC 7030, several endpoints, each with its own CA and rules. Intune challenge validation.
Discovery
Scan the network, find every certificate, tell the managed from the rest.
Deploy Hooks
Push renewed certificates and fresh CRLs to the hosts that serve them, over SSH, and reload.
HSM & Key Recovery
PKCS#11, Azure Key Vault, Cloud KMS. Archived keys come back under four eyes.
SSH CA
Sign user and host keys, ship the trust config as a one-line setup script.
CRL, OCSP & TSA
Delta CRL, delegated OCSP responder, RFC 3161 timestamping.
FIPS Mode
Preview. Cryptography in a CMVP-validated OpenSSL FIPS module, in Docker or natively on RHEL 9 and Ubuntu 24.04 Pro.
Policies
Allowed key types and signature hashes, approvals and alerts, on issuance, renewal and revocation.
Access Control
RBAC, LDAP/AD, OAuth2 and SAML SSO, mTLS, WebAuthn as second factor, IP allowlists.
Reports & Alerts
Scheduled PDF reports, expiry and policy e-mails, 15+ webhook events, syslog.
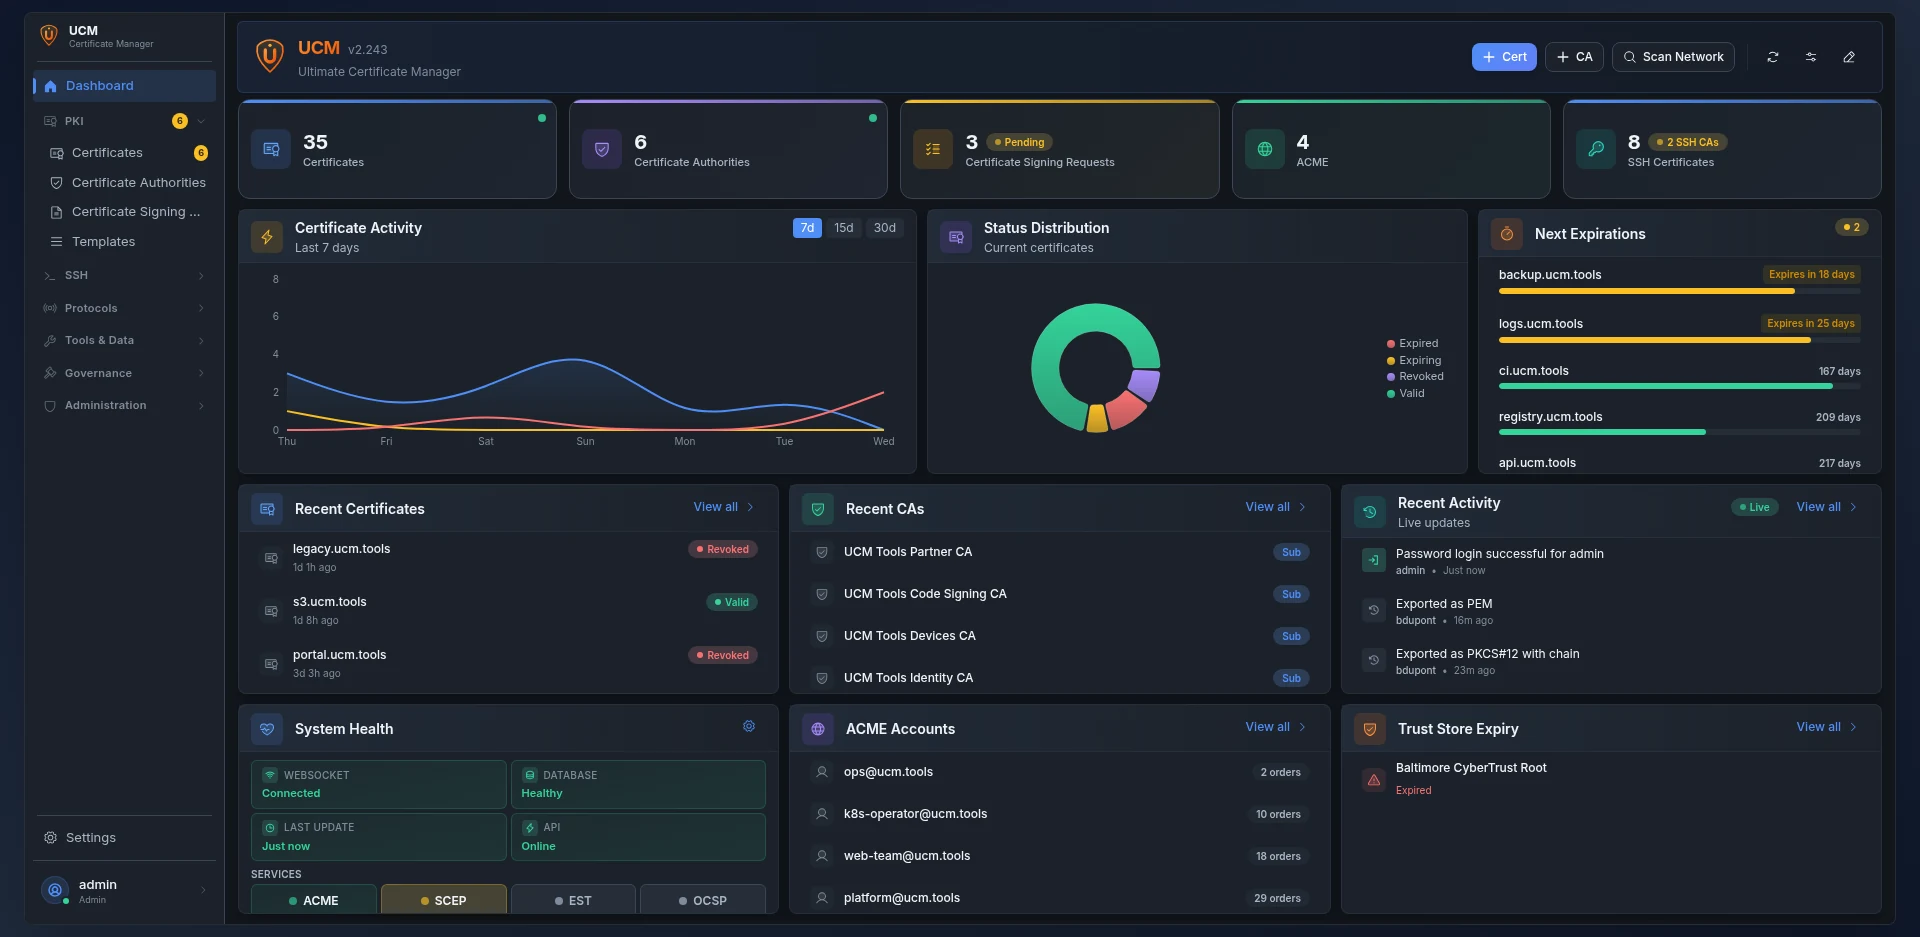
A UI you'll actually want to use
Not just a CLI with a web wrapper. A real, modern interface, on desktop and mobile.
Fully responsive
Manage your PKI from any device.